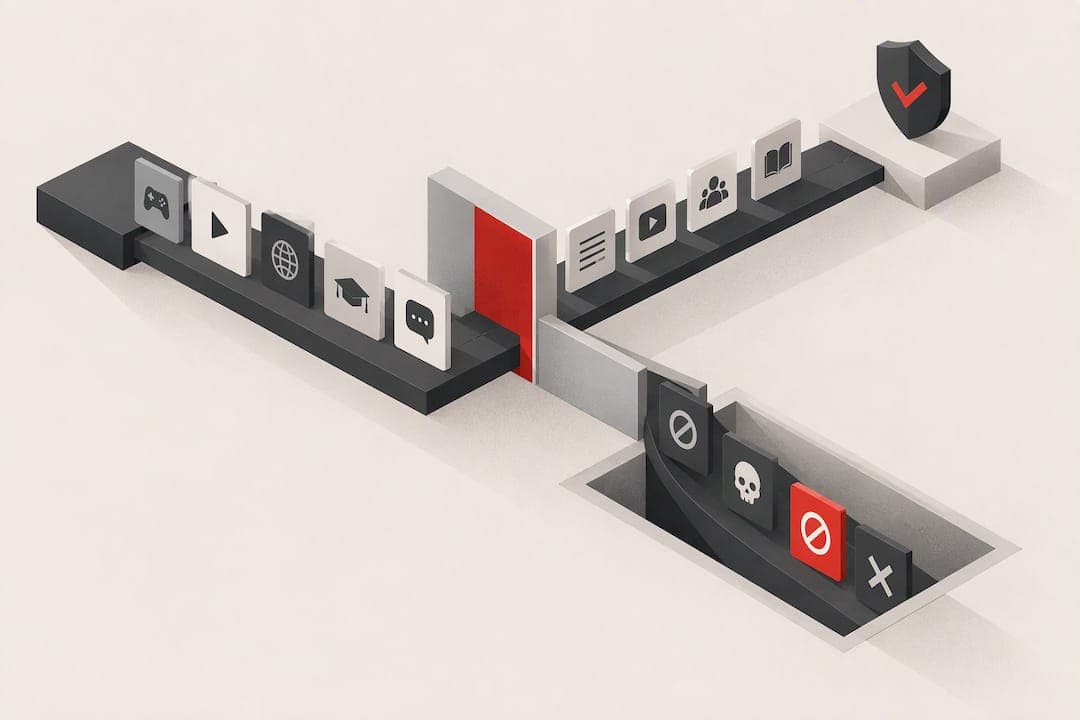
Allowlist means explicit allow, so anything not named is denied by default. Blocklist means explicit block, so anything not named is permitted by default. That single difference in default action makes allowlisting the stricter, more restrictive control and blocklisting the more permissive one, and it is why security teams increasingly favor the terms allowlist, denylist, and blocklist over older, less precise language.
TL;DR:
- Allowlisting is more restrictive but requires constant updates, making it ideal for fixed systems with stable software inventories.
- Blocklisting is easier to maintain and better suited for environments with constantly shifting content or internet-based access.
- Matching on cryptographic hashes or verified signatures enhances rule durability against renames and relocations.
- Combining allowlisting for critical assets with blocklisting for the broader network balances security and operational flexibility.
- Using clear, action-oriented language like allow, deny, permit improves policy clarity and future-proofing in documentation.
Table of Contents
- Definitions and why the default action matters
- Pros and cons compared
- Implementation considerations and hardening
- When to choose allowlist, blocklist, or both
- Terminology, inclusivity, and clear documentation
- Rolling out a list-based control without breaking production
- A security admin's take on picking a default
- FAQ
- Sources
Definitions and why the default action matters
The NIST glossary defines an allowlist as a documented set of specific entities approved by policy, where anything outside that set is denied. The NIST glossary defines a blocklist the opposite way: a documented set of entities blocked by policy, with everything else ordinarily permitted unless another rule says otherwise. The practical effect is the failure mode. An allowlist fails closed: a legitimate but unlisted item gets rejected, which is an availability problem. A blocklist fails open: an unlisted and unknown threat gets through, which is a security gap.
These patterns show up across common systems:
- Application control, where only approved executables or publishers are permitted to run.
- DNS filtering, where approved corporate domains sit on an allowlist and known-harmful domains sit on a blocklist.
- Email systems, where safe-sender lists let trusted senders bypass spam filtering.
- Content moderation, where allow and block lists govern which accounts or keywords are treated as trusted or prohibited.
Pros and cons compared
Both models solve the same problem from opposite directions, and each carries a distinct operational cost. Comparative analysis of the two approaches finds allowlisting stronger against unknown threats but heavier to maintain, since every legitimate addition needs an inventory update and approval step. Blocklisting is lighter to run and easier to adjust, but it only stops what it already knows to name, leaving new or renamed threats free to slip through.
- Allowlisting: strong against zero-day and unknown threats, but requires a maintained inventory and an exception process for every new legitimate item.
- Blocklisting: fast to deploy and easy to extend, but structurally reactive since it can only block what has already been identified.
- Operational drag: allowlists generate more false positives when the inventory lags behind real usage, while blocklists generate false negatives when threats change names, hashes, or domains.
Pro Tip: Treat the choice as a spectrum, not a binary: layer a tight allowlist around your most sensitive systems and a monitored blocklist around everything else.
Neither approach alone covers a full estate well, which is why most mature security programs run both at once, scoped to different assets.
Implementation considerations and hardening
The attribute you match on decides how durable the rule is. Filename or file path rules are brittle because an attacker can simply rename or relocate a file. The CISA application whitelisting guide recommends matching on cryptographic hashes, digital signatures, or verified publisher certificates instead, since those attributes survive a rename or a move.
Rollout matters as much as the rule itself. CISA's guidance points to staged deployment: a learning or alert-only mode first, then a limited pilot, then full blocking, each stage with a defined exception and appeal path so a legitimate tool is not locked out without recourse.
Once a list is live, feed its events into monitoring:
- Send allow and block events into your SIEM so a spike in denials surfaces quickly.
- Track false-positive rate, blocked-attempt volume, and time-to-resolve exceptions as standing metrics.
- Document list scope and precedence explicitly, since an undeclared default is a silent gap.
A DNS or gateway policy that never states its default action can let traffic through by accident when neither list applies, a point the Cloudflare DNS policy documentation makes explicit when it describes precedence rules between allow and block lists.
When to choose allowlist, blocklist, or both
The right default depends on how enumerable "good" is in that environment. A system with a small, stable set of approved software is a strong allowlist candidate. A system exposed to constantly shifting, user-chosen content is usually a blocklist candidate, because listing every acceptable item is impractical.
- Favor allowlisting for industrial control systems, servers, kiosks, and other critical infrastructure where the software set rarely changes.
- Favor blocklisting for general web filtering and BYOD endpoints, where enumerating every acceptable site or app is not realistic.
- Combine both by wrapping critical systems in a tight allowlist island while running blocklisting and monitoring across the broader, less controlled estate.
- Before adopting an allowlist, confirm you have an accurate software inventory, a change-control process, and staff able to handle exception requests, since a thin allowlist without those pieces creates more outages than it prevents.
Terminology, inclusivity, and clear documentation
Vendor and government style guidance has moved away from "whitelist" and "blacklist." The Microsoft style guide recommends allowlist and denylist, and the UK NCSC's terminology guidance argues the change improves clarity as well as inclusivity, since allow and deny describe the actual mechanism rather than a color metaphor. Google's developer style guidance adds a useful caution: not every "list" is literally a list, so documentation should describe the real action, such as "deny requests from this IP," rather than mechanically swapping one noun for another.
- Update policy documents and dashboards to the terms allowlist, denylist, and blocklist.
- Leave legacy code and API field names in place where renaming would break integrations, and add a comment mapping the old term to the current one.
- Prefer action-focused phrasing in rules and logs, such as "deny" and "permit," over list-noun shorthand.
Rolling out a list-based control without breaking production
A staged rollout keeps a new allowlist or blocklist from becoming an outage generator.
- Scope the control to a specific system or asset class and choose durable attributes such as hash, signature, or verified publisher rather than filename or path.
- Run a learning or alert-only phase long enough to capture normal variation, then review what would have been blocked.
- Pilot in blocking mode on a limited group before enabling it broadly.
- Define an exception and appeal process in advance, with a named owner and a target turnaround time.
- Track metrics continuously: false-positive rate, blocked-attempt counts, and time-to-resolve exceptions, feeding all of it into your SIEM.
Pro Tip: Never flip a new allowlist straight to blocking mode on a Friday. Pilot it on a small group first so the exception queue is manageable when something legitimate gets caught.
A security admin's take on picking a default

Default deny is the stronger instinct, and I would reach for an allowlist whenever the environment is enumerable: fixed server roles, kiosks, industrial control systems. Where the set of legitimate activity keeps shifting, a well-monitored blocklist paired with alerting is the more honest choice, since pretending you can enumerate the open internet only produces a brittle, half-finished allowlist.
What changes the outcome in practice is less the choice itself than the discipline around it: a staged rollout, a real exception process, and metrics that tell you when the list is drifting out of sync with reality. Clear, action-focused language in your policies and code (deny, permit, allow) also pays off quietly, since it keeps the next engineer from guessing what an old rule was supposed to do.
— Andrejs
FAQ
Is "allowlist" a real, standard word?
Yes. It is the term NIST and major vendor style guides, including Microsoft's, use in current technical documentation to describe an explicit-allow, deny-by-default list.
Is "whitelist" considered an outdated or problematic term?
Style guidance from organizations such as the UK NCSC favors allowlist and denylist because those terms describe the actual allow or deny action rather than relying on a color-based metaphor, and most major vendors have shifted their documentation accordingly.
What does an allowlist mean on a phone?
On a phone, an allowlist is a set of apps a parent or user explicitly permits, with everything else restricted by default. WalkBlock applies a related model by letting parents choose which apps stay restricted while a child is walking, while keeping essential tools like maps and calls accessible through a PIN-protected setting.
Is allowlisting more secure than blocklisting?
Allowlisting is generally the stronger control against unknown or new threats because it denies anything not explicitly approved, while blocklisting only stops what has already been identified. The tradeoff is maintenance: an allowlist needs an accurate, kept-current inventory and an exception process to avoid blocking legitimate activity.